Security of the software delivery process

Cybersecurity for technology companies
and regulated sectors

We address the technical requirements of
NIS2 UKSC DORA CRA ISO/IEC 27001 SOC 2

What changes in your company

You ship faster

Security stops being a gate you have to clear right before release. Controls run in the background, on every code change, without meetings or waiting for someone's sign-off.

Audits stop halting the work

A failed audit is not a bad grade on paper. It is a blocked deployment, a frozen contract, and a team that spends weeks collecting evidence in reverse instead of shipping. When evidence is produced automatically, the audit comes down to showing evidence you already have — not a company-wide standstill.

Costly surprises disappear

A vulnerability surfaces at code review, not in a customer report or a pentest two weeks before signing. At that point the fix costs a fraction of what it would later.

Three ways we work

CRA Platform

For manufacturers, importers and distributors of products with digital elements — compliance evidence kept separately for every version you ship.

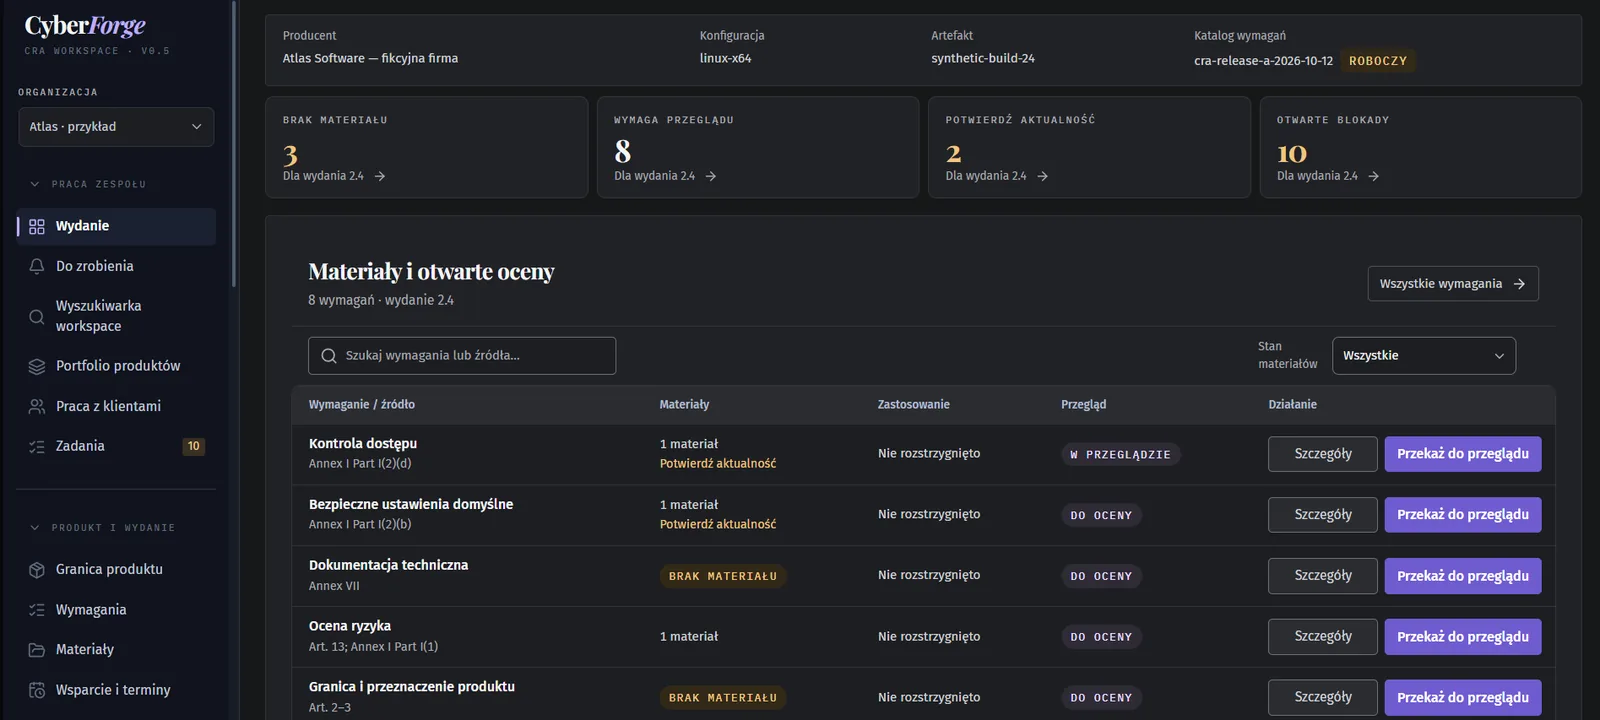
CRA Platform — product releases with their materials, gaps and decisions

Technical documentation and the declaration of conformity assembled from a release's own records, not written from scratch before an audit

Reporting deadlines of 24 h, 72 h and 14 days counted from awareness, with an owner, a deputy and a trace of every decision

SBOM in CycloneDX and SPDX, vulnerabilities tied to the version they actually affect, and a recorded impact assessment

An auditor package for one release: scope, materials and decisions, with a checksum manifest — the auditor can verify nothing has changed

Technology companies
and regulated sectors

Banks, fintechs, SaaS companies, software houses and software vendors — including organisations covered by NIS2, the Polish KSC Act, DORA and the CRA, and their suppliers, who end up under the same audit as a result. We close the technical layer of these requirements; you handle the organisational and legal part with your team and adviser — based on the evidence we leave behind.

Regulators ask about the process, not the policy

You have had procedures for years, but the questions go deeper: how the code is produced, who approves it, how you know that what reaches production is safe. We build evidence an auditor can verify.

  • Requirements for ICT systems and suppliers
  • Regulators expect evidence, not declarations
  • Board accountability for security

You grow faster than your process keeps up

You ship changes every day, because that is your business. Yet you face the same requirements as a bank that deploys once a quarter. We set up controls so you don't have to choose between speed and compliance.

  • Regulatory requirements with frequent releases
  • Third-party supplier risk
  • Operational continuity and resilience

Security is blocking your sales

A large client sent a questionnaire with hundreds of questions and the contract is on hold. Or they require a certificate you don't have. We close the gaps and prepare answers backed by evidence.

  • A questionnaire is holding up the signature
  • The client requires SOC 2 or ISO 27001
  • Selling to enterprises in the US, UK and DACH

Your product falls under new regulations

You sell products with digital elements in the EU. Since 11 September 2026 an actively exploited vulnerability must be reported within 24 hours — including in versions sold earlier. Add technical documentation and control over what enters your product from outside.

  • Vulnerability reporting obligations
  • Technical documentation and supply chain
  • Growing customer requirements

We work on recognized standards

We plug into what you already use. Your team keeps its way of working, we add only what is missing — and everything we implement stays with you.

Process maturity
OWASP SAMM · DSOMM · NIST SSDF The frameworks we use to measure the level of your delivery process — and what specifically moves it up a level.
Verification and testing
OWASP ASVS · Top 10 · WSTG A checklist of requirements you can tick off point by point. Enterprise clients usually ask directly about ASVS compliance.
Threat modeling
STRIDE · LINDDUN · PASTA The methods we use to find weak points at the design stage — before the first line of code exists.
Supply chain
SLSA · CycloneDX · SPDX · in-toto The formats and levels that let you prove exactly what ended up in your product and where it came from.
Management systems
ISO/IEC 27001 · SOC 2 · PCI DSS The certifications enterprise clients ask about. We address their technical part — your team and auditor handle the rest.

Fill in the form

We'll get back to you within 24 hours on business days. The call is free.